Built to be trusted with your books
Security is part of how the account works, from the first code we send you to every change our staff make.
Built to be trusted with your books
Security is part of how the account works, from the first code we send you to every change staff make.
One-time codes, never stored as typed
A verification code is kept only as a keyed hash. It expires in minutes, works once and locks after repeated wrong tries.
No passwords by email
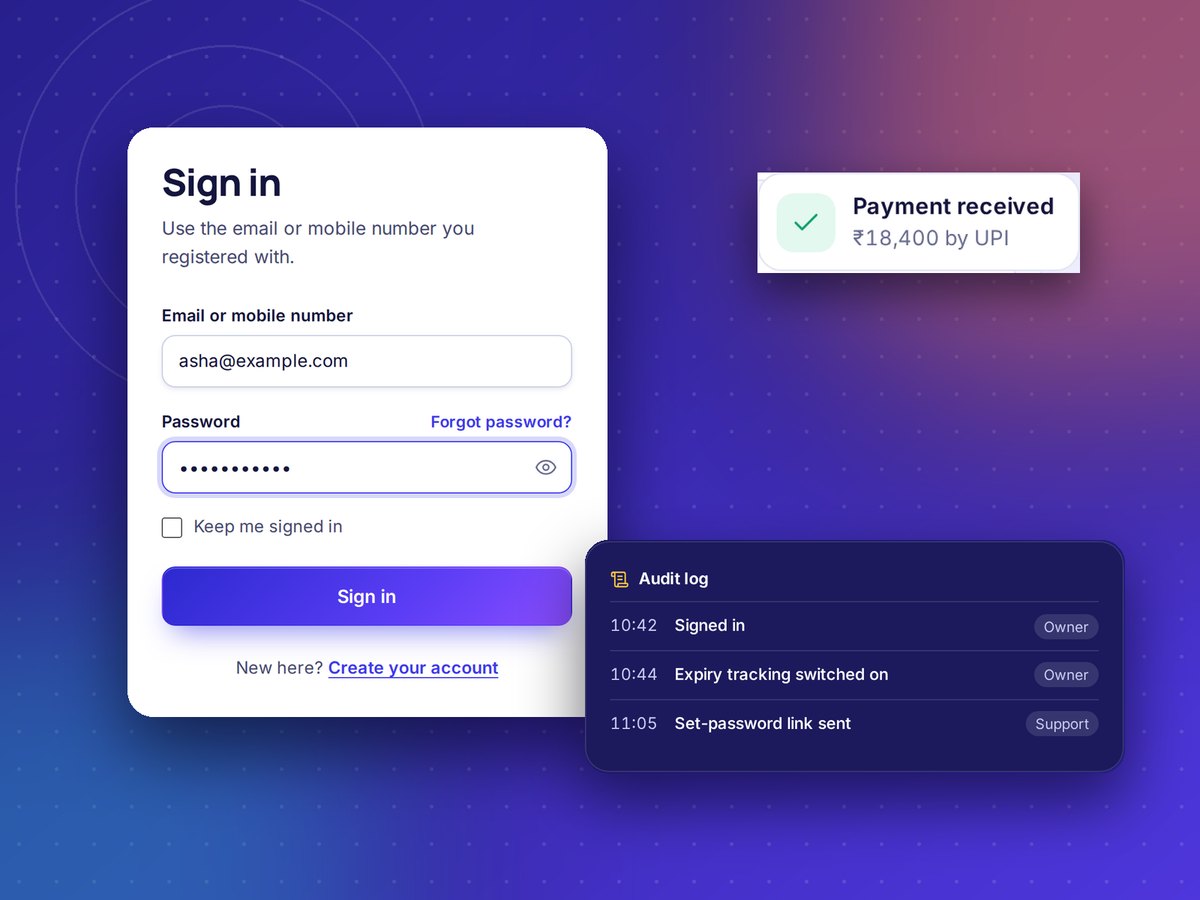
You choose your password through a single-use link. We never send or see it.
Passwords hashed, connection encrypted
Passwords are stored with a modern one-way hash, and the site is served over HTTPS.
Staff see only what they need
Support, Admin and Super Admin levels are checked on every action, and contact details stay masked by default.
A permanent audit log
Sign-ins, changes and staff actions are recorded with who, what and when. Entries cannot be edited or deleted.
Limits against misuse
Sign-in and code requests are rate-limited, and saved service keys are encrypted.
Your part in keeping the account safe
A few habits that keep your books private.
Never share a code
We never ask for your verification code. Anyone who asks for it is not us.
Use a strong password
At least 8 characters with a letter and a number; longer is better.
Sign out on shared devices
On a shop or family computer, sign out when you are done.
Keep your email safe
Password links go to your email, so protect that mailbox too.